Preventing CSRF Attacks in Modern Web Apps
How CSRF attacks exploit authenticated sessions and the layered defenses - anti-CSRF tokens, SameSite cookies, Referer validation, and secure frameworks - that stop them.
Articles in Uncategorized.
How CSRF attacks exploit authenticated sessions and the layered defenses - anti-CSRF tokens, SameSite cookies, Referer validation, and secure frameworks - that stop them.
How cross-site scripting attacks work, the three main types of XSS, their business impact, and the layered defenses that prevent them.
A developer-focused walkthrough of the OWASP Top 10 web application security risks, what each vulnerability means, and how to mitigate them across the development lifecycle.
Secure coding practices every front-end developer should know, from input validation and Content Security Policy to authentication token handling, CSRF protection, and dependency security.
Essential secure coding practices every web developer should adopt from the outset, from input validation and least privilege to automated security testing and dependency management.
How to choose an MBA program that matches your career goals: clarifying your objectives, picking a format, comparing specializations, faculty, alumni networks, ROI, and admissions requirements.
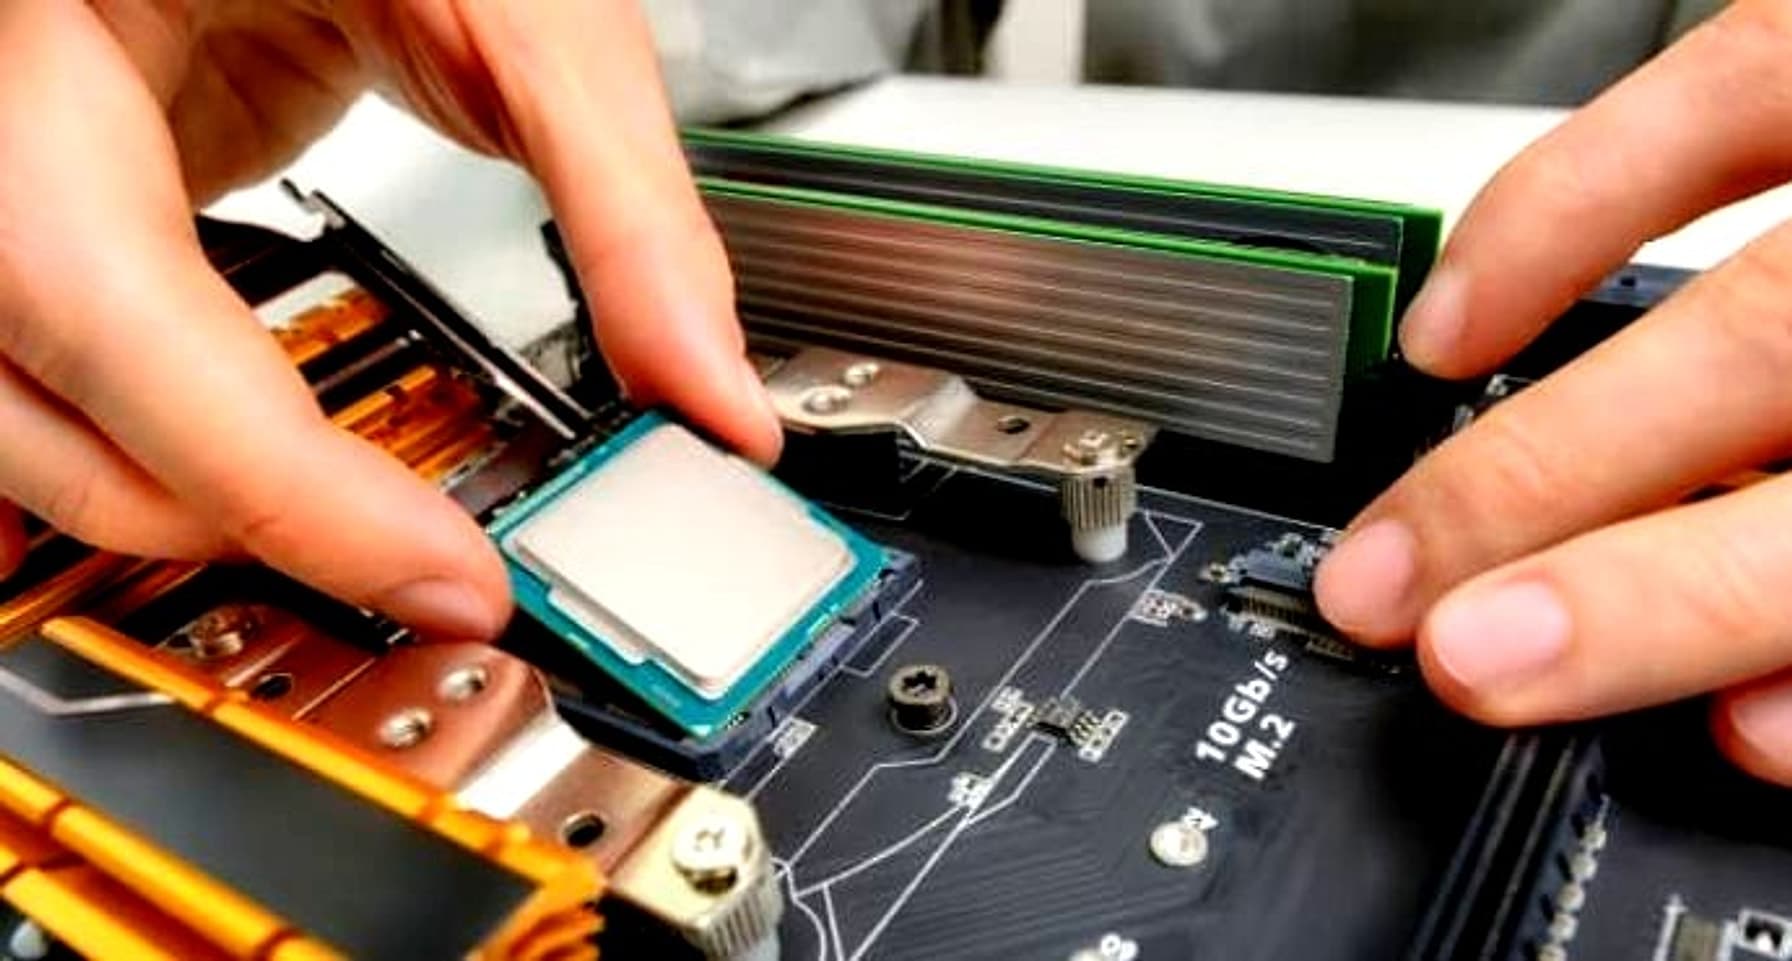
Discover which hardware upgrades, from RAM to storage to CPU cores, make the biggest difference in a developer's daily workflow and when the bottleneck lies elsewhere.
Wondering how to improve you website content quality? Here are the ten impactful tips to make your website content better.

Learn how to form a Wyoming LLC in 2026 with this simple step-by-step guide covering naming, filing, fees, EIN, and annual reports for new owners.